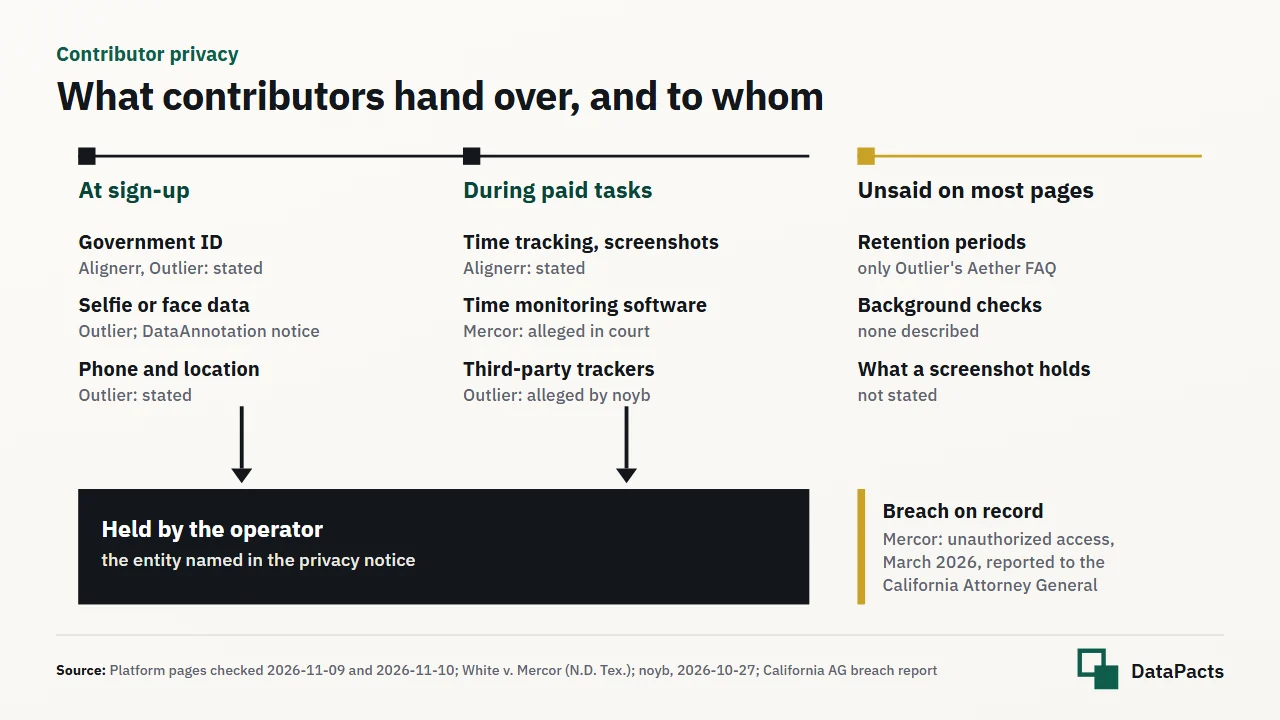
At least one company in this work, Mercor, has reported a breach of contributor data to a regulator, and a privacy group has filed complaints about another. This page lists what each platform states, what the record shows and which laws apply, each with a date and no verdict.
Contributors are the human route within AI training data licensing, where the people who produce the data hand over their own details first.
Platform pages were read on 2026-11-09, dockets are given as of 2026-11-09, and every breach or complaint comes from a company notice, a regulator or complainant filing or a court record. The fact-check note under the byline links the method.
What contributors hand over to AI training platforms, platform by platform
Each platform states a different set of checks on its own pages, from Alignerr's Persona ID verification and Hubstaff screenshots to DataAnnotation's privacy notice that allows facial recognition data, and the table lists them as each platform's claim, checked 2026-11-09.
The table compares six platforms by operator, identity checks, monitoring and other data terms, as of 2026-11-09 (Handshake's entity and Outlier's Aether FAQ checked 2026-11-10), in alphabetical order.
| Platform | Operator named on its pages | ID and biometric checks | Monitoring | Other data terms | Source | Profile |
|---|---|---|---|---|---|---|
| Alignerr | ALIGNERR LLC ("powered by Labelbox") | Persona ID verification; FAQ visa answer: only US identity documents accepted | Hubstaff time tracking with periodic screenshots | unlimited, irrevocable, perpetual, royalty-free, sublicensable right to use interview material | alignerr.com/en/faqs; alignerr.com/privacy | Alignerr |
| DataAnnotation | Surge Labs, Inc. dba DataAnnotation (court record) | privacy notice effective 2026-06-23 allows collection of facial recognition data from contractors | not recorded | no public terms of service; EU and UK representative Euverify Ltd | app.dataannotation.tech/da-privacy-policy | DataAnnotation |
| Handshake AI Fellowship | Stryder Corp. d/b/a Handshake and Handshake AI Solutions, LLC | not recorded | not recorded | privacy policy defines "Handshake" as Stryder Corp. d/b/a Handshake and affiliates | joinhandshake.com/privacy-policy | Handshake AI Fellowship |
| Mercor | Mercor.io Corporation | not recorded | complaint alleges time monitored by Insightful software (allegation, White v. Mercor) | security incident of March 2026 (see the privacy record below) | courtlistener.com; mercor.com blog | Mercor |
| Outlier | Scale AI, Inc. and Smart Ecosystem Inc. | valid ID and mobile phone from country of residence; ID and location verification; VPN prohibited; Aether FAQ names Persona as ID verification provider (ID images plus a selfie, checked 2026-11-10) | not recorded on own pages; trackers alleged by noyb | Aether onboarding 15 to 60 minutes plus about 20-minute Outlier Interview; confidentiality survives termination (s.5) | outlier.ai/faq; outlier.ai/legal/terms-of-use; outlier.ai/aether-faq | Outlier |
| Shipd | Datacurve AI, Inc. (Contributor Terms; operator in privacy policy last updated 2026-06-01) | not recorded | not recorded | privacy policy says Work Product is assigned to Datacurve, Inc., a second entity name | shipd.ai/terms; shipd.ai/privacy | Shipd |
The operator named in the privacy notice or terms is the party that holds the contributor's data. Shipd's privacy policy names Datacurve AI, Inc. as operator, as its Contributor Terms do, but says Work Product is assigned to Datacurve, Inc., so two entity names appear for one platform.
A contributor who wants to ask for access or deletion therefore starts from the entity named in the privacy notice, not from the brand on the sign-up page.
Identity and biometric checks: ID documents, face checks and who runs them
Identity checks on AI training platforms ask for a government ID and, at some platforms, a face image or video matched against it, run inside the platform's sign-up flow before any paid task.
Outlier states that it requires a valid ID and a mobile phone from the contributor's country of residence, verifies ID and location, and prohibits VPN use, according to its FAQ and Flexible Working Guidelines (checked 2026-11-09).
Providers are named for some platforms and not others. Alignerr's FAQ lists Persona ID verification in its sign-up steps, and its visa answer accepts only US identity documents. DataAnnotation's privacy notice, effective 2026-06-23, allows collection of facial recognition data from contractors and names no provider in the pages read.
Outlier's Aether FAQ names Persona as its identity verification provider, collecting images of the ID plus a selfie (checked 2026-11-10), and noyb's complaints allege repeated face videos and ID uploads through Persona for Outlier workers; that is an allegation, not a finding.
Face data is biometric data under GDPR Art. 9(1) when it is processed to identify a person uniquely, and its processing is prohibited unless an Art. 9(2) exception applies. The law table below sets out the other rules that reach these checks.
Monitoring software during paid tasks: time trackers, screenshots and device trackers
Three kinds of monitoring appear on the record: Alignerr states it tracks time with Hubstaff and periodic screenshots, a complaint against Mercor alleges time monitored by Insightful software, and noyb alleges that Outlier placed third-party trackers on workers' devices.
The first is a platform statement checked 2026-11-09, and the other two are allegations that no court or authority has decided as of 2026-11-09. A statement about a tool is not a statement about how it is configured, so the three are kept apart in the contributor-data table.
In White v. Mercor.io Corporation (N.D. Tex. 6:26-cv-00201-H), the amended complaint of 2026-06-25 alleges unpaid time monitored by Insightful software, and the case is pending. noyb lists TikTok, LinkedIn, Facebook, Sprig and Datadog trackers in its complaints of 2026-10-27, and Outlier's own pages name no tracker tool for paid tasks.
The pages read do not say what a screenshot captures, how often it is taken, who can see it or how long it is kept. Monitoring terms sit beside pay and IP terms in AI training jobs and platforms compared.
Background checks and retention periods: what platform pages leave unsaid
None of the platform pages read for this page describes a criminal, credit or employment background check, and only Outlier's Aether FAQ states how long ID or interview data is kept. The absence is a statement about the pages read on 2026-11-09, not a statement about what a platform does.
Outlier's Aether FAQ describes onboarding of about 15 to 60 minutes plus an online interview of about 20 minutes, and states that interview recordings are deleted after seven days (up to 90 days for an account under review) and verification data is kept for up to two years after the last interaction (checked 2026-11-10).
Outlier's Terms of Use say that confidentiality survives termination (s.5), which is a duty on the contributor and not a retention rule.
Colorado's HB 24-1130, effective 2025-07-01, shows what a stated rule looks like: it requires a written retention schedule, an incident protocol and deletion guidelines for biometric identifiers. No period is given here for the other platforms, because none is published on their pages read.
Breaches and data protection complaints that affected contributors
Two records concern contributor data directly: Mercor's report of unauthorized access in March 2026 and noyb's five GDPR complaints of 2026-10-27 against Scale AI over Outlier. The table lists each dated record, with its type and status as of 2026-11-09, in chronological order.
| Date | Company | Record (type) | What it concerns | Status (as of 2026-11-09) | Source |
|---|---|---|---|---|---|
| 2026-03-24 and 2026-03-30 | Mercor.io Corporation | breach report to the California Attorney General (regulator filing) | unauthorized access through compromised LiteLLM versions | reported 2026-06-25 | oag.ca.gov breach report sb24-625431; consumer notice |
| 2026-05-08 | Mercor.io Corporation | White v. Mercor.io Corporation, N.D. Tex. 6:26-cv-00201-H (court) | misclassification; unpaid time monitored by Insightful software (allegations) | pending; amended complaint 2026-06-25 | courtlistener.com Dkt. 16 |
| 2026-05-19 | Mercor.io Corporation | In re Mercor.io Corporation Data Breach Litigation, N.D. Cal. Lead Case No. 3:26-cv-02821-WHO (court) | negligence and related claims over the March 2026 breach (allegations), putative class of contractors and job applicants | consolidated 2026-05-19 (ECF 29); stay pending mediation stipulated 2026-07-21 (Dkt. 44); no ruling on the merits | archive.org RECAP Dkt. 44 |
| 2026-06-25 | Mercor.io Corporation | security incident update and consumer notice (company notice) | notices to affected experts 2026-06-25 and 2026-06-26; 24 months of TransUnion credit monitoring offered | enrollment deadline 2026-10-01 passed | mercor.com blog; oag.ca.gov consumer notice |
| 2026-10-05 | Mercor.io Corporation | Consumer Privacy Ombudsman's Supplemental Report, Bankr. S.D.N.Y. 25-11897 (SHL), Dkt. 1684 (court-appointed review) | further research requested into Mercor's security incident | sale not approved; hearing 2026-11-17 (Dkt. 1779) | courtlistener.com Dkt. 1684 |
| 2026-10-27 | Scale AI, Inc. (Outlier) | five GDPR complaints by noyb with Intérêt à Agir, DIPLab and Reversing.Works (complainant filing) | trackers, data minimization, Persona biometric checks, unanswered access requests (allegations) | filed; no reference numbers published; no decision found | noyb.eu |
The register of incidents naming companies that buy AI training data, with breaches, regulator complaints and court reviews, sits in data buyer incidents, dated and sourced; this page keeps to what the records mean for contributors.
The Mercor security incident of March 2026, from the contributor side
Mercor.io Corporation reported to the California Attorney General that unauthorized access through compromised versions of the open-source LiteLLM library occurred on 2026-03-24 and 2026-03-30, and it sent notices to affected experts on 2026-06-25 and 2026-06-26. Mercor states that "a very limited subset" of its "nearly five million" experts had sensitive information affected, which is the company's claim.
The consumer notice offered 24 months of TransUnion credit monitoring with enrollment by 2026-10-01, a date that has passed.
The suits are consolidated as In re Mercor.io Corporation Data Breach Litigation, stayed pending mediation since the stipulation of 2026-07-21, with no ruling on the merits as of 2026-11-09. In the Spirit Airlines bankruptcy, the Consumer Privacy Ombudsman's report of 2026-10-05 asked for further research into the incident.
noyb's five GDPR complaints over Outlier contributor data
noyb states that on 2026-10-27 it filed five GDPR complaints against Scale AI over Outlier, with Intérêt à Agir, DIPLab and Reversing.Works, before authorities in France, Italy, the Netherlands and Austria.
The complaints allege trackers on workers' devices, data minimization failures, Persona biometric checks and unanswered access requests, and they ask for an investigation and a fine. noyb states that Outlier has more than 900,000 workers; no decision or reference number is published as of 2026-11-09.
Laws that reach contributor ID checks and monitoring
Rules on biometric data and on monitoring apply to contributors through where they live and how the platform processes their data, not through the label contractor or employee. The table compares six rules by provision and start date, as of 2026-11-09.
| Instrument | Provision | What it says | Applies from | Source |
|---|---|---|---|---|
| GDPR, Regulation (EU) 2016/679 | Art. 9(1) | processing of biometric data for uniquely identifying a person is prohibited unless an Art. 9(2) exception applies | 2018-05-25 | eur-lex.europa.eu |
| GDPR | Art. 88(2) | national employment rules must include safeguards with regard to monitoring systems at the workplace | 2018-05-25 | eur-lex.europa.eu |
| Illinois BIPA, 740 ILCS 14 | 14/15(b), 14/15(c) | written notice and written release before collecting biometric identifiers; no profiting from them | in force; amended effective 2024-08-02 (P.A. 103-0769) | ilga.gov |
| Colorado Privacy Act as amended by HB 24-1130 | C.R.S. 6-1-1301 et seq. | written retention schedule, incident protocol and deletion guidelines; consent before collecting biometric identifiers | 2025-07-01 | leg.colorado.gov |
| Washington, RCW 19.375 | 19.375.020(1), 19.375.030(2) | notice and consent before enrolling biometric identifiers for a commercial purpose; enforced by the attorney general only | 2017 | app.leg.wa.gov |
| EU Platform Work Directive, Directive (EU) 2024/2831 | Art. 29 | Member States transpose by 2026-12-02 | transposition 2026-12-02 | eur-lex.europa.eu |
GDPR Art. 88(2) names workplace monitoring systems in the employment context only, and the Directive's rules on monitoring are not described here, only its transposition date. For the Illinois statute in full, see Illinois BIPA and AI training data, which sets out the notice, release and damages rules.
Sharing ID and accepting monitoring: benefits, risks, downsides and alternatives
ID checks and monitoring are the price of access to most AI training platforms, and the trade is between paid, flexible work and personal data held by a company that has to keep it safe. The four lists below weigh the choice neutrally, as of 2026-11-10.
Benefits
- An identity check ties the account to a named person, which supports paid time records.
- Platforms that track time, such as Alignerr, hold a record of the hours worked.
Risks
- A breach can expose contributor data: Mercor reported one on 2026-06-25.
- Biometric processing is contested: noyb's complaints allege Persona face and ID checks for Outlier.
- Unpaid time monitored by Insightful software is alleged in White v. Mercor.
Downsides
- Only Outlier's Aether FAQ states retention periods on the pages read.
- Alignerr takes a perpetual right to use interview material, with no obligation to pay for the interview.
- DataAnnotation publishes no terms of service that were found on 2026-11-09.
Alternatives
- Platforms that state fewer checks on their pages.
- Participant panels for research studies.
- Employed roles with a named employer.
- Not taking the work at all, which is a valid outcome.
Steps before handing over ID and after a breach notice
Reading the privacy notice date and the named operator before verification, and acting on a breach notice by its stated deadline, are the two points where a contributor has the most control.
Neither step promises any outcome, and the notice itself is the contributor's only dated record of what the platform said it would do with the data.
Before handing over ID:
- Read the date of the privacy notice and the operator it names, as DataAnnotation's notice (effective 2026-06-23) and Shipd's two entity names show.
- Look for an EU or UK representative where one is named, such as Euverify Ltd in DataAnnotation's notice.
- Read the time-tracking and screenshot terms, such as Alignerr's Hubstaff statement.
After a breach notice:
- Read the notice and note its deadlines.
- Enroll in any offered monitoring before the stated deadline, as Mercor's notice set 2026-10-01.
- Keep the notice and the date it arrived.
How this page is compiled: platform pages, notices, dockets and statutes only
Every statement here comes from a platform's own pages, a company notice, a regulator or complainant filing, a court docket or a statute, each with the date it was read.
Platform pages were checked on 2026-11-09, with Outlier's Aether FAQ re-read on 2026-11-10, and dockets are as of 2026-11-09, following how we source, date and check every figure. Forums, review sites and press are never sources, and this page is information, not legal advice.
Where contributor privacy meets the rest of human data work
This page covers what platforms collect and lose about contributors; the pages below cover the companies, legitimacy checks, lawsuits, classification and privacy law by jurisdiction.
- human data for AI: the companies
- is AI training work legit: ID requests outside a platform's own site are a scam sign
- contributor lawsuits against human data platforms
- privacy law and AI training data
- contractor or employee
- Mercor data breach class actions
- noyb complaints against Scale AI (Outlier)
- how DataPacts is funded: no platform pays for a place on this page
Frequently asked questions
Does Outlier use Persona for ID verification?
Yes: Outlier's Aether FAQ names Persona as its identity verification provider (checked 2026-11-10). Alignerr names Persona for itself. noyb's complaints about repeated Persona checks are allegations.
Can an AI training platform take screenshots while I work?
Yes, a platform can state that it does: Alignerr states Hubstaff time tracking with periodic screenshots (checked 2026-11-09). The other platforms' pages name no screenshot tool for paid tasks, and no page published what is captured.
How do I know whether my data was in the Mercor breach?
Mercor sent notices to affected experts on 2026-06-25 and 2026-06-26, and the notice is the confirmation. DataPacts offers no lookup of any breach.